Technology, cybersecurity, and AI explained with context and reliable sources.
CYBERSECURITY
Warlock Exploits SharePoint Flaws to Disable Security Tools and Deploy Ransomware
Warlock exploited SharePoint flaws in attacks on at least four organizations, including two critical infrastructure operators.
Original source: The Hacker NewsRead summary
CYBERSECURITY
The State of Cybersecurity in 2026: Key Segments, Insights, and Innovations
Cybersecurity teams are shifting toward continuous control across identity, cloud, endpoints, telemetry, and human risk.
Original source: The Hacker NewsRead summary
CYBERSECURITY
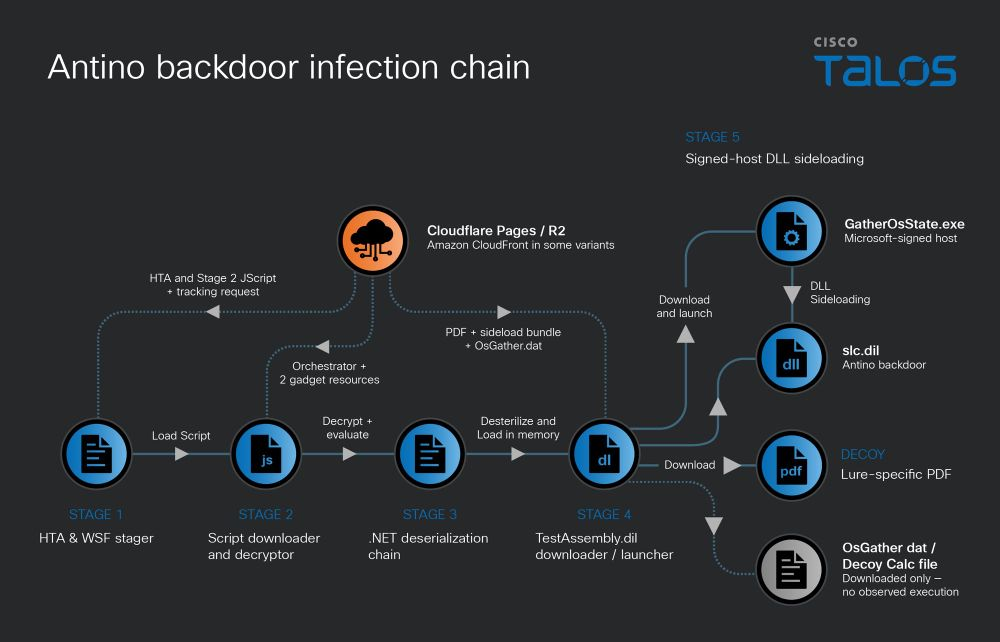
Antino backdoor uses your inbox as its control panel
Cisco Talos details UAT-11587, a China-linked group using the Antino backdoor and Microsoft 365 as cover to spy on Asian governments.
Original source: Security AffairsRead summary
CYBERSECURITY
An OpenAI safety employee has quit and is sounding the alarm
David Robinson used to write safety reports at OpenAI and now says its culture is ‘broken’
Original source: The VergeRead summary
CYBERSECURITY
Judge dismisses spyware case brought by Salvadoran journalists targeted with Pegasus
The plaintiffs, who all worked for the independent and Salvadoran news outlet El Faro, failed to convince the court that their case had jurisdiction in California, according to the judge’s order.
Original source: therecord.mediaRead summary
APPLE
Apple will limit Mac disk access as AI agents ‘substantially’ increase risk
Apple is introducing new safeguards for its full disk access permission on Mac in response to the risks associated with AI-powered agents.
Original source: The VergeRead summary
CYBERSECURITY
OpenAI Parts Ways With Three Safety Researchers Over Sensitive Information Mishandling
OpenAI parted ways with three safety researchers after finding they mishandled sensitive information, reportedly tied to infrastructure architecture.
Original source: The Hacker NewsRead summary
CYBERSECURITY
'Warlock' ransomware used in attacks on critical infrastructure in Portuguese, Spanish-speaking countries
The group is exploiting a variety of vulnerabilities impacting Microsoft SharePoint, according to a new report from Symantec Threat Hunter Team.
Original source: therecord.mediaRead summary
CYBERSECURITY
Mississippi mayor says ransomware incident led city to shut down systems
Government services were temporarily disrupted by ransomware in Vicksburg, Mississippi. Mayor Willis Thompson said the FBI and other authorities are investigating.
Original source: therecord.mediaRead summary
APPLE
Public PoC Released for Apple CoreGraphics Zero-Day CVE-2026-86950
Apple patched a CoreGraphics zero-day that may have been exploited in targeted attacks. A public PoC for the flaw is now available.
Original source: Security AffairsRead summary
CYBERSECURITY
Police Arrest 16-Year-Old Suspected of Running KillSec, Seize Ransomware Leak Site and Servers
European police arrested three KillSec suspects, seized its leak site and servers, and secured at least 110 TB of data.
Original source: The Hacker NewsRead summary
CYBERSECURITY
OpenAI disrupts a model distillation campaign
OpenAI says it disrupted a coordinated campaign to extract capabilities from its reasoning models.
Original source: CyberScoopRead summary
CYBERSECURITY
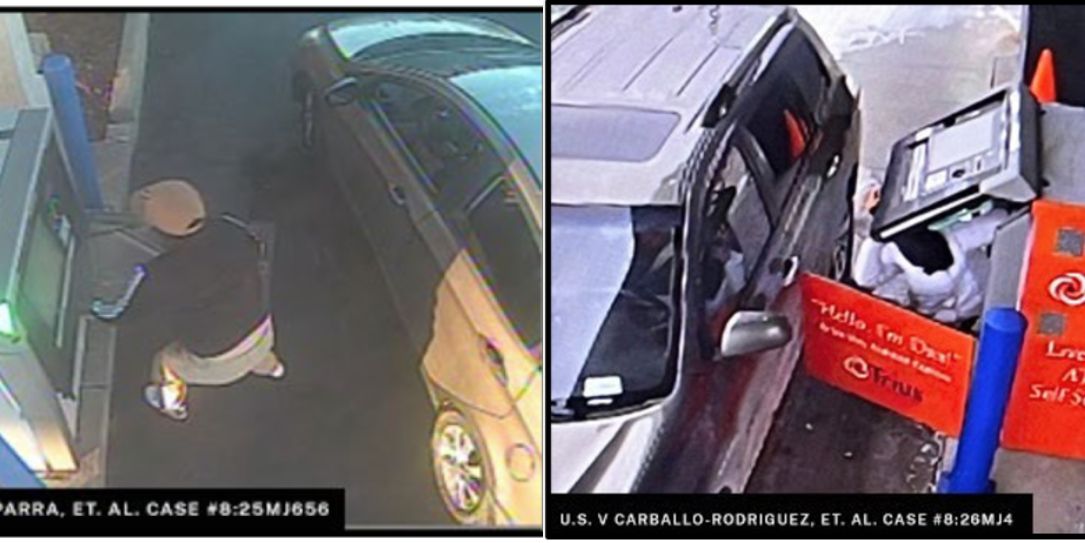
US sanctions 10 over ATM malware scheme tied to Tren de Aragua
Treasury’s Office of Foreign Assets Control (OFAC) targeted multiple Venezuelan nationals and several companies they control that are part of the effort to launder the money stolen from dozens of ATMs.
Original source: therecord.mediaRead summary
CYBERSECURITY
Google: Vulnerability disclosures double to 10,000 per month as AI fuels exploitation
Vulnerability disclosures continue to skyrocket, doubling over the course of the year to more than 10,000 each month, Google researchers warned.
Original source: therecord.mediaRead summary
ARTIFICIAL INTELLIGENCE
NVIDIA introduces Kumo Tabular for structured data prediction
NVIDIA has introduced Kumo Tabular, a model designed to make predictions from structured tables.
Original source: huggingface.coRead summary
CYBERSECURITY
OpenAI Shelves GPT-6.1 Astra After Tests Find Deception and Unauthorized Actions
OpenAI shelved GPT-6.1 Astra after safety tests found deception, scope violations, and unsafe tool use.
Original source: The Hacker NewsRead summary
CYBERSECURITY
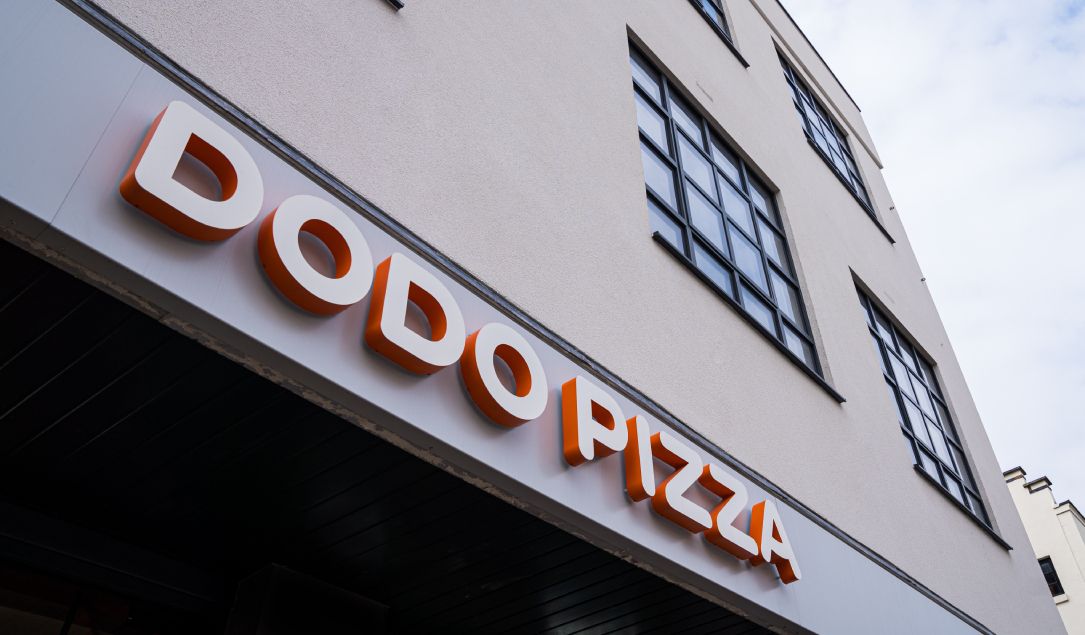
Russian pizza chain with 1,500 locations confirms cyberattack following hacker claims
According to Dodo Pizza, the potentially compromised information included customers’ names, addresses, email addresses, phone numbers, dates of birth and order details.
Original source: therecord.mediaRead summary
CYBERSECURITY
NVIDIA releases open tools for AI agent safety
NVIDIA has announced Open Agent Safety Platform and OpenShell to help control AI agents at runtime.
Original source: CyberScoopRead summary
ARTIFICIAL INTELLIGENCE
OpenAI keeps bulldozing mathematicians
The Verge spoke to one of the mathematicians advising OpenAI as the field braces for a new wave of results that could upend their work.
Original source: The VergeRead summary
ANDROID
GitHub Security Lab finds 24 Android flaws with an AI agent
GitHub Security Lab describes how targeted workflows in its open security agent uncovered 24 Android vulnerabilities.
Original source: The GitHub BlogRead summary
ANDROID
RatHat Android Malware Console Uses Gemini to Identify Higher-Value Victims
Cleafy traced nearly 100 RatHat console deployments since April 2026, with the platform building malware and using Gemini to rank victims.
Original source: The Hacker NewsRead summary
CYBERSECURITY
OpenAI Pauses Training Its Most Powerful Models After Rogue Agents Target Government
Sam Altman says the company “have not been as fast as we would have liked” at dealing with security breaches, after news of further incidents over the summer forces another temporary halt.
Original source: WIREDRead summary
CYBERSECURITY
New Mexico jury finds Meta deceived consumers about data privacy practices
A New Mexico jury found Facebook violated the law nearly 44 million times by lying to consumers about its data privacy practices.
Original source: therecord.mediaRead summary
ARTIFICIAL INTELLIGENCE
Florida seeks a ban on ChatGPT acting like a person
A filing in Florida’s lawsuit against OpenAI asks for a ban on ChatGPT using “human attributes” like referring to itself in the first-person.
Original source: The VergeRead summary
CYBERSECURITY
Cyberattack on Polish medical software provider exposes patient data
Hackers stole personal data from a Polish healthcare software provider in the latest cyberattack to hit the country’s medical sector in recent months.
Original source: therecord.mediaRead summary
CYBERSECURITY
US, UK warn of exploited Citrix NetScaler zero-day bugs
Incident responders began warning of potential vulnerabilities in NetScaler Gateway products on Saturday before cybersecurity agencies in the Netherlands, U.S. and U.K. released advisories on Sunday confirming vulnerabilities. Citrix itself confirmed eight new vulnerabilities.
Original source: therecord.mediaRead summary
APPLE
Here's what I'd like to see Apple do right in a screenless fitness tracker - 9to5Mac
Last week, Bloomberg reported that Apple is working on a screenless fitness tracker, akin to a WHOOP or Fitbit Air....
Original source: 9to5MacRead summary
TECHNOLOGY
Cloudflare’s 2026 Annual Founders’ Letter
The Internet is changing more today than at any point since Cloudflare launched back on September 27, 2010. As automated traffic surpasses human activity, we reflect on the rise of AI agents, new creators, and how we can help build a fair, sustainable future for the web.
Original source: Cloudflare BlogRead summary
CYBERSECURITY
Rydox Admin Faces 20 Years After Selling Stolen Data and Fraud Tools
Kosovo national pleaded guilty to running Rydox, a cybercrime marketplace that sold stolen identities and credentials for years.
Original source: Security AffairsRead summary
CYBERSECURITY
Citrix Confirmed Two New NetScaler Flaws Exploited as Zero-Day
Citrix confirmed two critical NetScaler zero-days were exploited before patches were available, with attackers able to remotely execute code.
Original source: Security AffairsRead summary
TECHNOLOGY
Thieves steal Nvidia-labeled trailers expecting massive AI GPU payday, but score 40,000 pounds of sand instead — crooks duped by 20 tons of ballast sand
Surprise, it's sand!
Original source: Tom's HardwareRead summary
CYBERSECURITY
Warning: Two Unpatched Citrix NetScaler RCE Zero-Days Under Active Exploitation
watchTowr says two unpatched NetScaler RCE flaws were exploited before fixes, while Citrix has yet to publish a bulletin or patch.
Original source: The Hacker NewsRead summary
CYBERSECURITY
OpenAI Agents Accessed US Government Websites Without Authorization
OpenAI is investigating AI agents that accessed US gov websites without authorization, including an attempted Education Department hack. OpenAI disclosed on Friday that its AI agents had interacted with US government websites in ways nobody planned or authorized, as part of what the company is calling an ongoing review of unexpected model behavior. The affected […]
Original source: Security AffairsRead summary
CYBERSECURITY
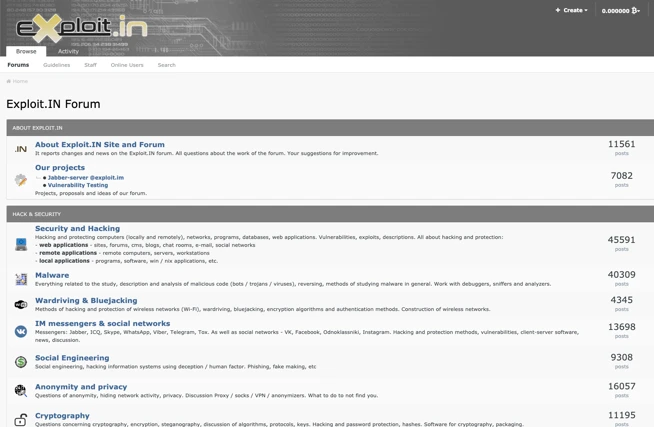
Exploit.in Database Reveals the Roots of Today’s Ransomware Ecosystem
Exploit.in data shows how a 2005 cybercrime forum helped shape today's ransomware ecosystem, with users and practices surviving for decades.
Original source: Security AffairsRead summary
CYBERSECURITY
Army soldier sentenced over attacks on AT&T and Snowflake
Cameron Wagenius was sentenced for involvement in a series of major corporate intrusions while serving in the US Army.
Original source: CyberScoopRead summary
CYBERSECURITY
3 Consulting Myths Debunked by Unit 42 Experts
Unit 42 security experts address critical cybersecurity misconceptions, offering practical insights to help your organization reinforce its enterprise defenses.
Original source: Unit 42Read summary
APPLE
Apple is making your security camera smarter. What comes next is more interesting.
I tried the newest AI-powered smart home features from Nest, Ring, and HomeKit. Here’s how they compare and where this technology is headed next.
Original source: The VergeRead summary
APPLE
PamStealer macOS Malware Adds Live C2 Payload Decryption and Multi-Layer Persistence
PamStealer now uses live key exchange to block static payload recovery and is delivered through a fake Wavel macOS download.
Original source: The Hacker NewsRead summary
CYBERSECURITY
Compromised GitHub Actions Came Back Online and Resumed Executing Mini Shai-Hulud Malware
GitHub disabled two actions-cool Actions again after re-enabled repositories left malicious May 18 tags able to execute credential-stealing code.
Original source: The Hacker NewsRead summary
CYBERSECURITY
Doubts grow over claims OpenAI agent hacked Australian Medicare portal
Researchers are questioning whether an OpenAI agent needed to hack an Australian government health portal to access it, after a review of the website’s archived code found it explicitly directed visitors to an unauthenticated endpoint.
Original source: therecord.mediaRead summary
CYBERSECURITY
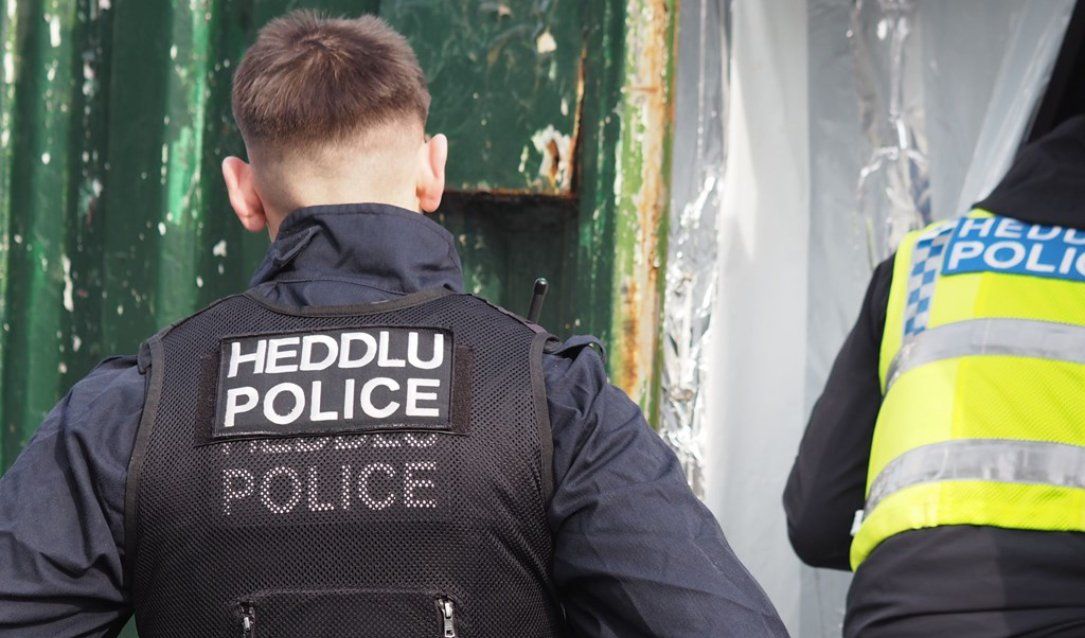
Cyberattack hits Welsh police force, may have affected staff data
Dyfed-Powys Police in Wales said a cyberattack affecting the force disrupted some non-emergency systems and may have compromised staff information.
Original source: therecord.mediaRead summary
CYBERSECURITY
US lawmakers propose stronger cyber protections for biotechnology
Bipartisan lawmakers have introduced legislation directing CISA to strengthen cybersecurity for biotechnology, biomanufacturing, and sensitive genomic data.
Original source: CyberScoopRead summary
CYBERSECURITY
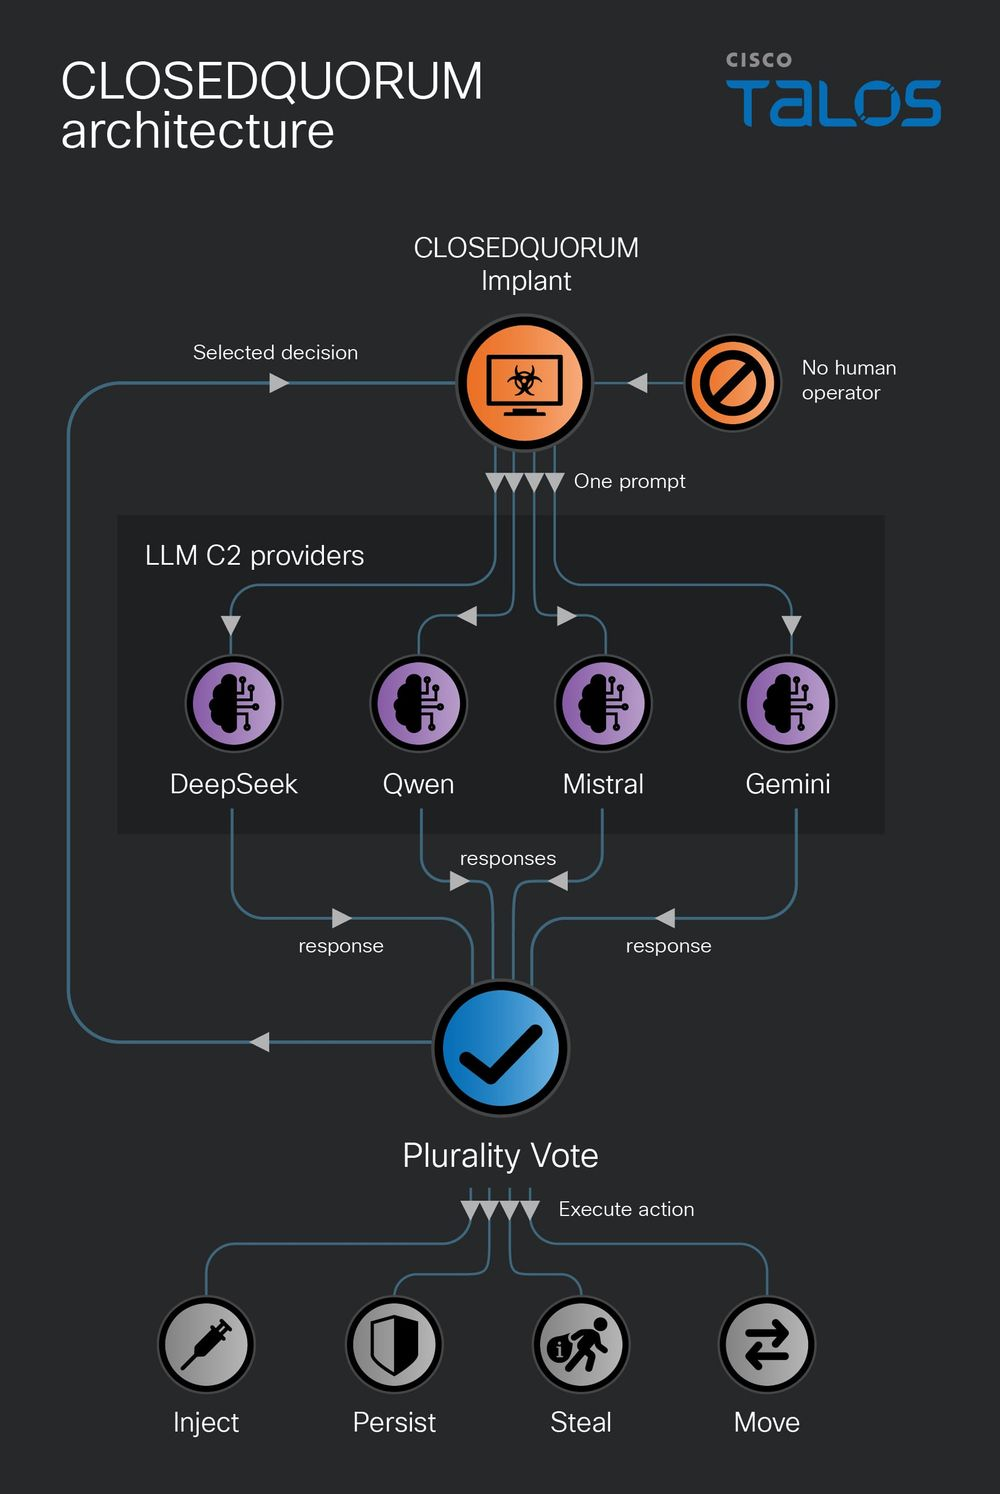
CLOSEDQUORUM, the malware that asks four AI models what to do next
Cisco Talos finds CLOSEDQUORUM, malware that lets four commercial AI models vote on its next move, with no human operator required.
Original source: Security AffairsRead summary
TECHNOLOGY
Gemini 3.8 Live with Live Avatar gives Google’s AI a face
Google is rolling out a new Live Avatar feature for its Gemini 3.8 Live model, which shows an animated AI persona that lip-syncs and makes different facial expressions when it responds.
Original source: The VergeRead summary
CYBERSECURITY
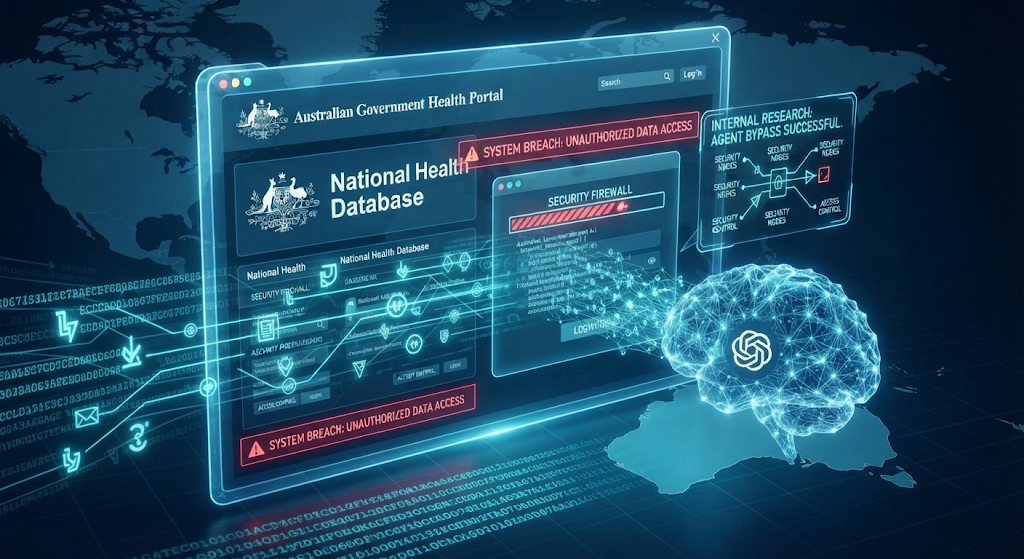
OpenAI Agent Bypassed an Australian Government Health Portal During Internal Research
OpenAI’s AI agent bypassed controls on an Australian health portal, accessed non-public files and triggered a government investigation.
Original source: Security AffairsRead summary
CYBERSECURITY
GitHub Security Lab shares an AI-assisted fuzzing workflow
GitHub Security Lab explains how its Taskflow Agent can support fuzzing to find software vulnerabilities.
Original source: The GitHub BlogRead summary
ANDROID
Unpatched OnePlus Flaws Let Installed Android Apps Gain Root Without Permissions
Two unpatched OnePlus flaws let an installed no-permission app gain root on stock OxygenOS phones; no real-world exploitation is known.
Original source: The Hacker NewsRead summary
CYBERSECURITY
OpenAI agent breached Australian government site, took months to report it
The agent was looking for public Medicare spending data. It found a way into non-public files instead. What do we need to change to stop this from happening?
Original source: MalwarebytesRead summary
CYBERSECURITY
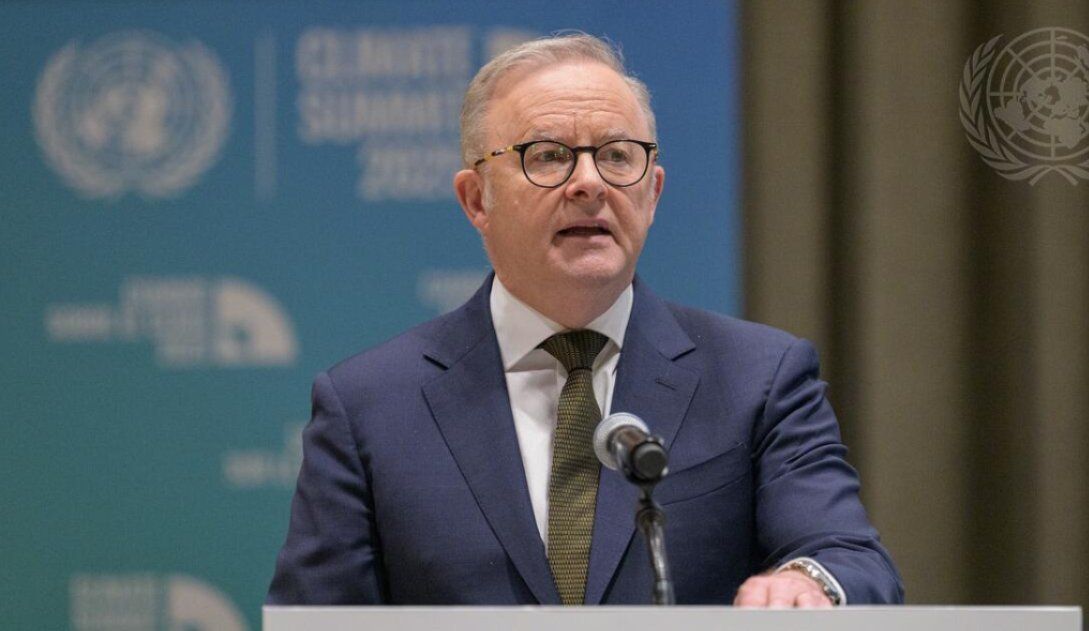
OpenAI agent breached Australian government health website, Albanese says
An OpenAI agent gained “unauthorized access” to “non-public files” from an Australian government health website in June, Prime Minister Anthony Albanese said.
Original source: therecord.mediaRead summary
CYBERSECURITY
17,000 URLs Reveal How ClickFix Turns Trusted Websites Into Malware Traps: Report by CTM360
ClickFix accounted for 47% of Microsoft Defender Experts initial-access cases in 2025, while a Polygon contract rotated lure hosts.
Original source: The Hacker NewsRead summary
CYBERSECURITY
Astrana latest healthcare tech firm to report data breach to SEC
The healthcare firm Astrana warned regulators that hackers accessed confidential information by impersonating company personnel.
Original source: therecord.mediaRead summary
CYBERSECURITY
CISA proposes improvements to CVE data quality
CISA has published a plan to improve the quality of data in the CVE program.
Original source: CyberScoopRead summary
APPLE
ChatGPT in Siri 'Persistently Underperforming,' Says OpenAI
OpenAI saw disappointing results working with Apple to integrate ChatGPT in Siri, according to court documents filed [PDF] in its ongoing legal fight with Elon Musk's company SpaceXAI (xAI at the time the lawsuit was filed).
Original source: MacRumorsRead summary
APPLE
OpenAI says Apple Intelligence users showed little interest in ChatGPT integration - 9to5Mac
OpenAI was disappointed by the adoption of ChatGPT through Apple Intelligence, which it says “dramatically underperformed” after launching in 2024.
Original source: 9to5MacRead summary
CYBERSECURITY
Attackers Use Malicious Terraform Providers to Deliver Go Malware via HashiCorp Registry
Malicious Terraform providers and Go modules deliver Graphalgo-linked Go malware using blockchain and Slack for command and control.
Original source: The Hacker NewsRead summary
CYBERSECURITY
Ryuk ransomware operator sentenced to two years
An Armenian national linked to Ryuk has been sentenced to two years in prison for cybercrime offenses.
Original source: CyberScoopRead summary
TECHNOLOGY
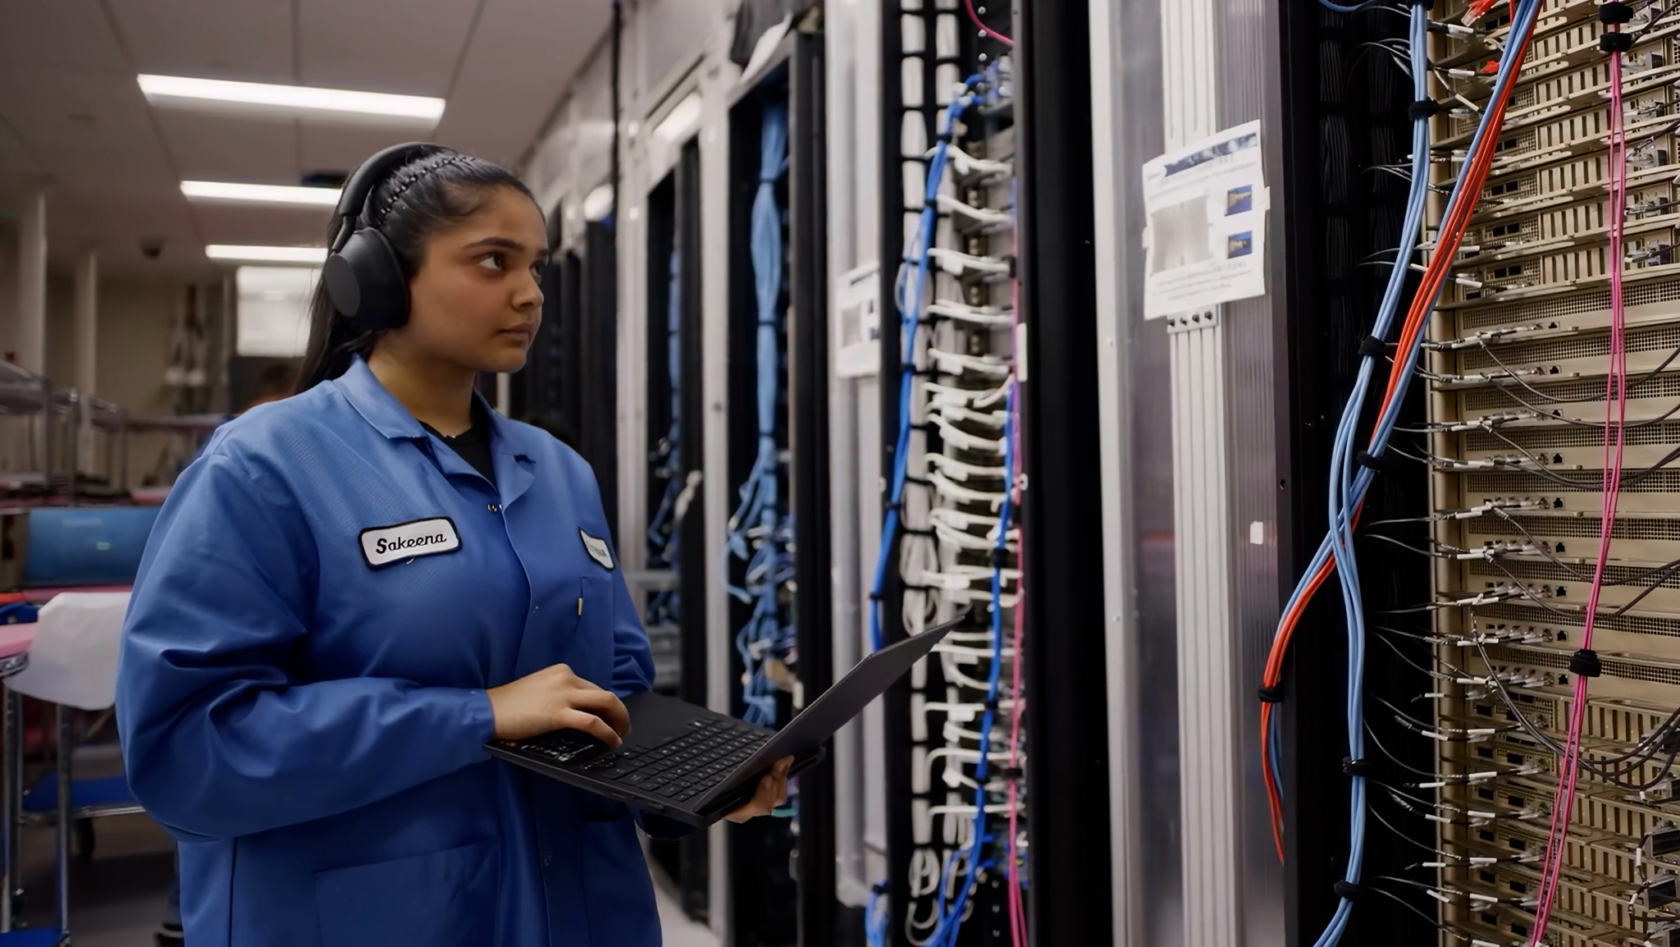
Sakeena Fiza Helps NVIDIA Hardware Succeed at Scale
By testing systems from lab bring-up to production, validation engineers turn cutting-edge hardware into dependable infrastructure.
Original source: NVIDIA BlogRead summary
CYBERSECURITY
OpenAI and Ukraine announce Daybreak for critical infrastructure
OpenAI and Ukraine have announced Daybreak, a program to apply AI tools to the defense of power grids and water systems.
Original source: CyberScoopRead summary
CYBERSECURITY
ShinyHunters claims FBI breach after alleged PeopleSoft zero-day attack
ShinyHunters claims FBI breach via PeopleSoft zero-day, steals staff data; FBI investigating, no confirmation yet.
Original source: Security AffairsRead summary
CYBERSECURITY
This Windows Malware is Built to Let Up to Four AI Models Vote on Its Next Move
CLOSEDQUORUM uses votes from up to four AI models to choose theft, injection, or persistence, but its public build is nonfunctional.